Storm Cloud Security
-
Storm Cloud Security Blog
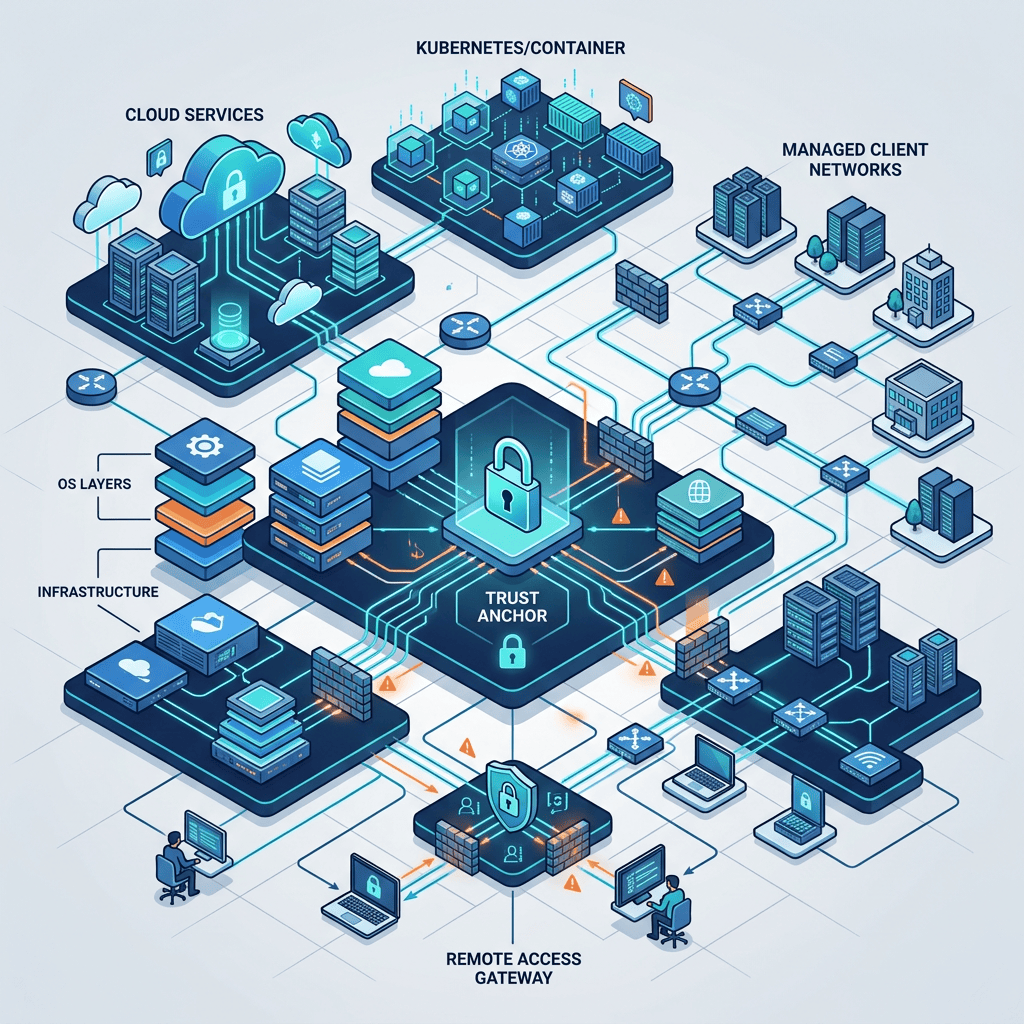
Compromised eMudhra Intermediate Certificates: Operational Risk for Managed Service Providers and Cloud Environments Published: October 21, 2026Author: Storm Cloud Security On October 17–20, 2026, the cybersecurity community identified a severe failure in the Web public key infrastructure (WebPKI). Eight intermediate certificate authority (CA) certificates issued by India-based eMudhra Limited (operating under the emSign brand) were…
-
Essential Security for Cloud Storefronts: Protect Your Business Data
In the rush to launch or scale a cloud-based storefront, many small businesses treat their IT service provider, e-commerce platform, hosting company, or managed service provider as a black box. You pay the invoice, the site stays online, and transactions process. That approach is no longer tenable. Your storefront holds customer names, addresses, payment details,…
-
Storm Cloud Security Blog: C-SCRM Series: Part 1 – Knowing Your Suppliers
Effective Cybersecurity Supply Chain Risk Management (C-SCRM) begins with a thorough understanding of your suppliers. As organizations increasingly rely on external vendors for critical hardware, software, and services, these third parties become integral extensions of the enterprise attack surface. A compromise at any point in the supply chain can have significant downstream impacts. This article,…
-
Securing the Chain
Securing the Chain: 3 Basic Considerations for Cyber-Supply Chain Risk Management (C-SCRM) in the Military Hey there, friends and partners in the defense community! At Stormcloud Security, we’re all about making cybersecurity approachable, practical, and—most importantly—effective for the folks who protect our nation every day. That’s why we’re thrilled to kick off a brand-new blog…
-
Major Chinese-Attributed Cyberattacks on Companies in 2025
As a professional cybersecurity controls assessor, I have reviewed available sources to identify the most significant cyberattacks attributed to Chinese state-linked actors in the past year (December 2024 to December 2025) that have notably impacted corporate cybersecurity. These incidents primarily involve espionage, data exfiltration, and disruption, often targeting critical infrastructure and private sector entities. Attribution…